[ Shipped Nov 4, 2026 ] Idea #88
Sandbox Check
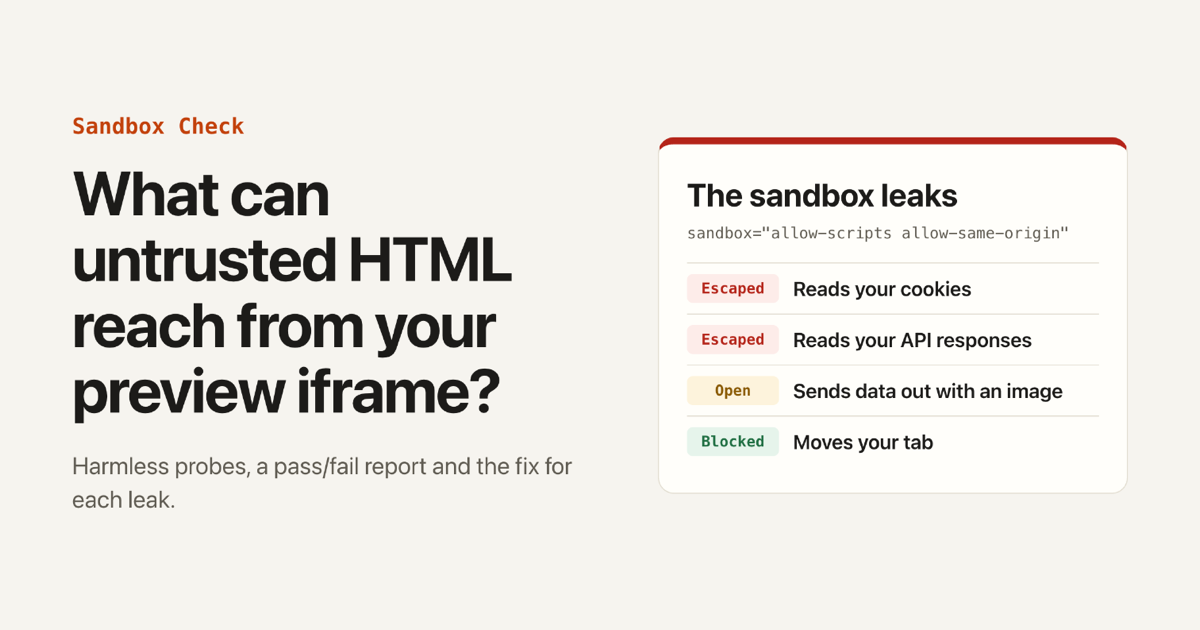
What can untrusted HTML reach from your preview iframe? Set up a frame the way your chat app or artifact feature renders model-written HTML, and a probe page inside it tries, harmlessly, to read your cookies, call your API, send data out, submit forms and move your tab. You get a pass/fail report with the fix for each leak.
The pitch
A small test harness that renders LLM-generated HTML the way chat apps do (sandboxed iframes, srcdoc, blob URLs) and runs a battery of harmless probes: cookie access, postMessage abuse, top navigation, and fetches to the parent origin. It outputs a pass/fail report for devs building their own artifact or preview feature.
Why now
Parameter Labs just showed account takeover through ChatGPT's HTML previews, and the lawyer prompt-injection sanctions show how far untrusted model output is spreading. Anyone building an artifacts-style feature needs a quick checklist.
Sparked by
- How We Took Over ChatGPT Accounts
- Parameter Labs' write-up
- Brazilian Court Sanctions Lawyers for Prompt Injection in Court Filing
The factory pitched this as “Artifact Sandbox Escape Kit: Test Your HTML-Preview Iframes.” Devin built and shipped it from that spec.